

What the Risk Score is
The Risk Score is a number from 0 to 100 that summarizes a client’s security posture. Higher is better. It is the main number on a Risk Assessment’s overview, and the one clients usually ask about in a QBR. Telivy calculates it with a harmonic penalty model, a formula that turns the severity and number of open findings into a score. Closing a few low-impact issues cannot inflate it much.This page covers Risk Assessments, which combine agent-based endpoint scanning with Microsoft 365 and Google Workspace data. External Assessments are scored differently.
What you see in the portal
When you open a Risk Assessment, the main dashboard shows:- A Risk Score gauge from 0 to 100, colored from red for low scores to green for high ones.
- The risk band (Critical, High, Medium, or Low) next to the gauge.
- A sparkline of recent scans, once the assessment has at least two completed scans. Until then it reads “Enable monitoring to track score history”.
- Top Actions, the findings that would raise the score most if fixed.
- CIS Controls Passing, a separate percentage explained below.
Risk bands
Each score falls into a risk band. Reports, exports, and score history all use the band:
With clients, lead with the band. “Your environment is rated Medium Risk” matches what they will see in the report.
How the score is calculated
In plain terms
In plain terms
Every finding has a severity: Critical, High, Medium, or Low. Higher severities subtract more from the score. Telivy adds up the penalty for all open findings and converts the total into a 0 to 100 number.Critical findings hit the score much harder than low-severity ones, and fixing any finding, even a low-severity one, always improves it. Larger environments are measured against higher expectations, so a 200-device client with 10 open findings loses fewer points than a 10-device client with the same 10. Platforms you haven’t connected, such as Microsoft 365 or Google Workspace, are left out of the score entirely.
Technical detail
Technical detail
The Risk Score uses a harmonic penalty model:Penalty accumulation:
Each finding contributes a penalty based on its severity weight:
Environment normalization:
Each penalty contribution is normalized against
maxExpected = perEntityCap × entityCount, where entity count is derived from the number of devices, users, domains, and web-facing hosts. Larger environments are not penalized just for having more assets.Platform filtering:
Controls with a platformRequirement of m365 or gws are filtered out if the corresponding integration is not connected. Filtered controls do not contribute to the score in either direction.Monotonic improvement guarantee:
The penalty function uses log(1 + rawCount/maxExpected) with no hard caps. Every remediation reduces the penalty, which always increases the score. There is no threshold below which fixing a finding has no effect.The CIS Controls Passing percentage shown alongside the gauge is a separate calculation: positiveBlocks / totalBlocks × 100, where a block is considered passing if it has no open findings. It is not derived from the harmonic penalty model and is not the number displayed in the Risk Score gauge.CIS Controls Passing
Next to the Risk Score, the dashboard shows a CIS Controls Passing percentage. It is a separate metric.
A client can have a high Risk Score and a low CIS Controls Passing percentage when their open findings are spread across many low-severity controls. A single Critical finding can pull the Risk Score down while most CIS controls stay green.
Use CIS Controls Passing when the conversation is about compliance frameworks, and the Risk Score when it is about business risk.
Top Actions
The Top Actions table ranks findings by how much fixing them would raise the Risk Score. It shows:- Finding category and severity
- Number of affected assets
- Score Gain, the points the Risk Score would increase if this finding were fully remediated
- Action type (auto-fix available, requires configuration, manual remediation)
Score history
Once an assessment has at least two completed scans, score history shows up in two places:- The sparkline on the Risk Score card, covering recent scans.
- Risk Score Over Time, a full chart on the Risk tab covering every scan.
Why the score changes between scans
A scan can find issues that were not there before, such as a newly published CVE, a configuration change, or a new device, and those lower the score. Resolved findings stop counting and raise it. The score can also move when the findings stay the same. Adding or removing devices, users, or domains changes the size baseline the penalty is measured against. Telivy also adjusts severity weights and normalization from time to time and announces those changes in the release notes.Risk Priority Score
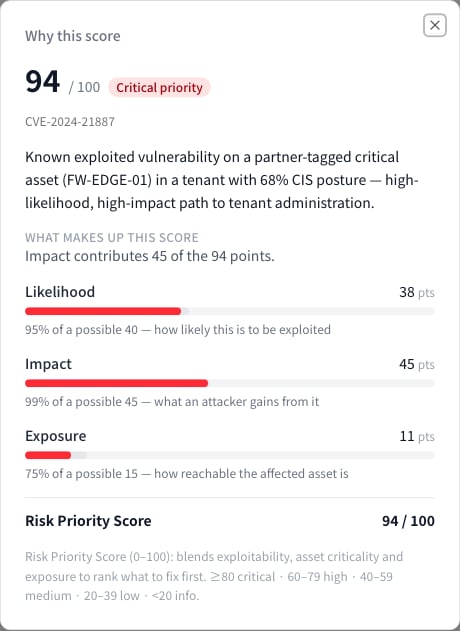
The Risk Score describes the whole environment. The Risk Priority Score (RPS) answers a different question: which vulnerability to fix first. Every CVE finding, and every device with CVEs, gets an RPS from 0 to 100 that combines three factors:
The RPS falls into a priority band:
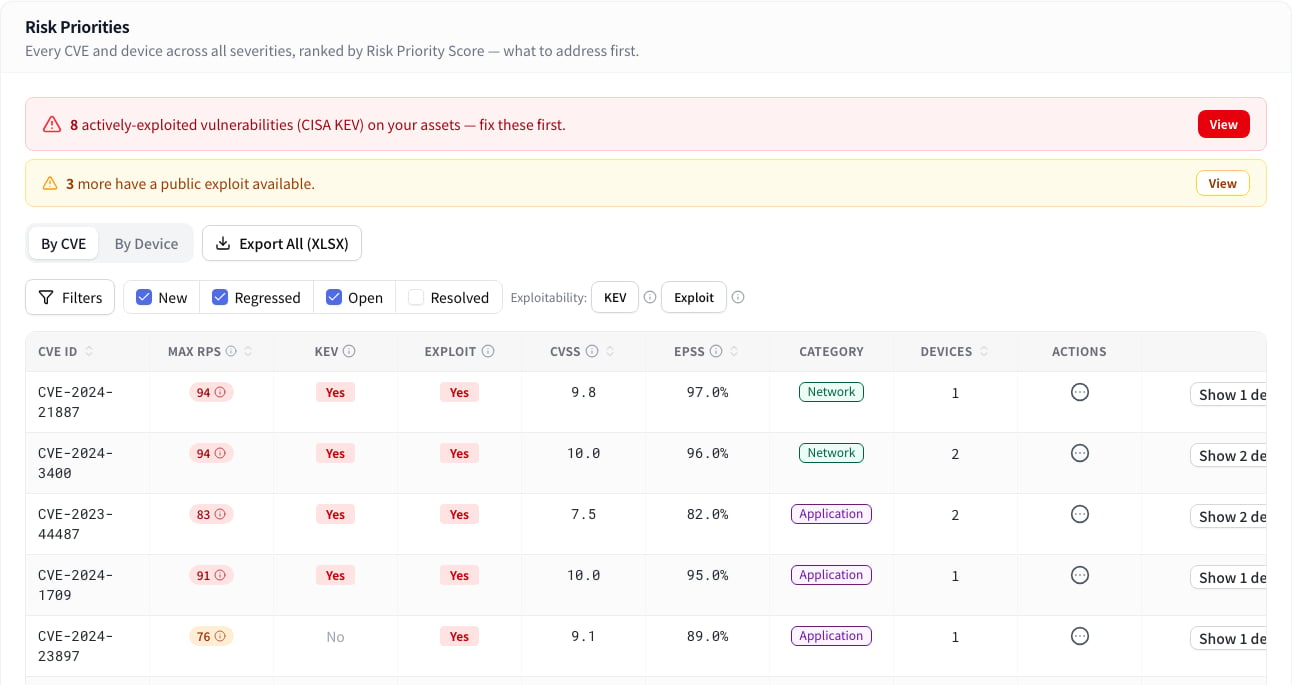
RPS appears in the RPS column on the Priorities tab (every CVE and device across all severities, ranked by RPS), on the Risk tab, in the vulnerability tables under Security, and on the Endpoints table under Inventory. Where a row groups several findings, such as a device, the column shows the highest RPS in the group.
Adjusting the RPS weights
The RPS is a weighted sum:RPS = weight × Likelihood + weight × Impact + weight × Exposure. To change how much each factor counts for a client, open the assessment, select More, and choose Risk Scoring Weights. Each weight must stay within its allowed range, and the three must add up to 1.00. Save stores them as an override for that company. The dialog shows where the current weights come from (Company override, Agency default, or System default), and Reset to defaults removes a company override.
FAQ
Why do two similar-looking environments have different scores?
Why do two similar-looking environments have different scores?
Two environments that look alike can still differ in their findings, in which platforms are connected (Microsoft 365, Google Workspace), and in their number of assets. Size matters too: a 10-device client and a 200-device client with the same types of findings get different scores, because expectations scale with the environment.
My score dropped but I didn't change anything. Why?
My score dropped but I didn't change anything. Why?
The most common cause is a newly published CVE in software that was already installed. New devices or users also change the size baseline, and scoring model updates can shift the number. Model updates are listed in the release notes.
Does accepting or resolving a finding affect the score?
Does accepting or resolving a finding affect the score?
Yes. Accepted and resolved findings are left out of the score. Accepting a finding records a deliberate decision by you or the client to live with that risk.
How often is the score recalculated?
How often is the score recalculated?
Every time a scan completes, whether you started it or monitoring did. The score always reflects the most recent scan.
What's the difference between Risk Score and CIS Controls Passing?
What's the difference between Risk Score and CIS Controls Passing?
The Risk Score is weighted by severity and adjusted for environment size. CIS Controls Passing is the share of applicable controls with no open findings. They measure different things and can move independently. See CIS Controls Passing.
Will the scoring model change over time?
Will the scoring model change over time?
Yes. Telivy updates severity weights, normalization, and control mappings from time to time, which can shift scores. Changes are announced in the release notes.