

Finding the results
1
Open Network Security
Open the assessment’s Security tab and go to Network Security. It works the same way on External Scans and Risk Assessments.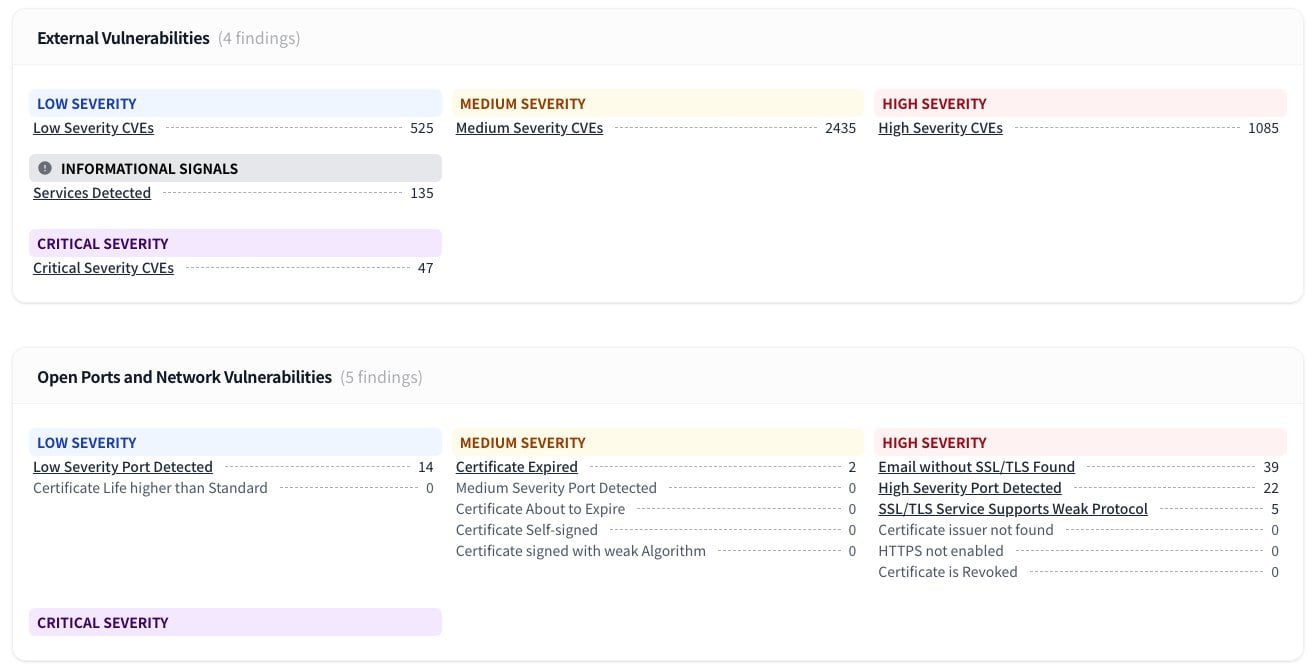
2
Find the finding
Email without SSL/TLS Found is listed in the Open Ports and Network Vulnerabilities card, under its severity.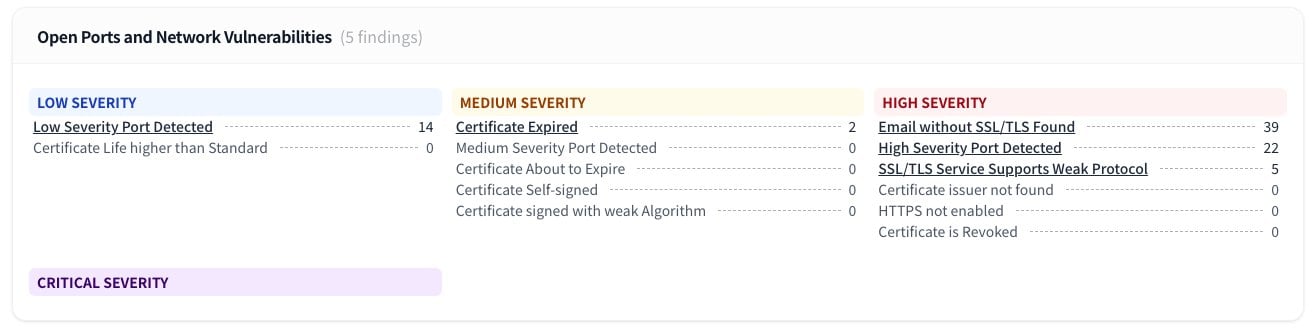
3
Review the ports
Click the finding to see the recommendation and the domains and ports that accept unencrypted mail traffic.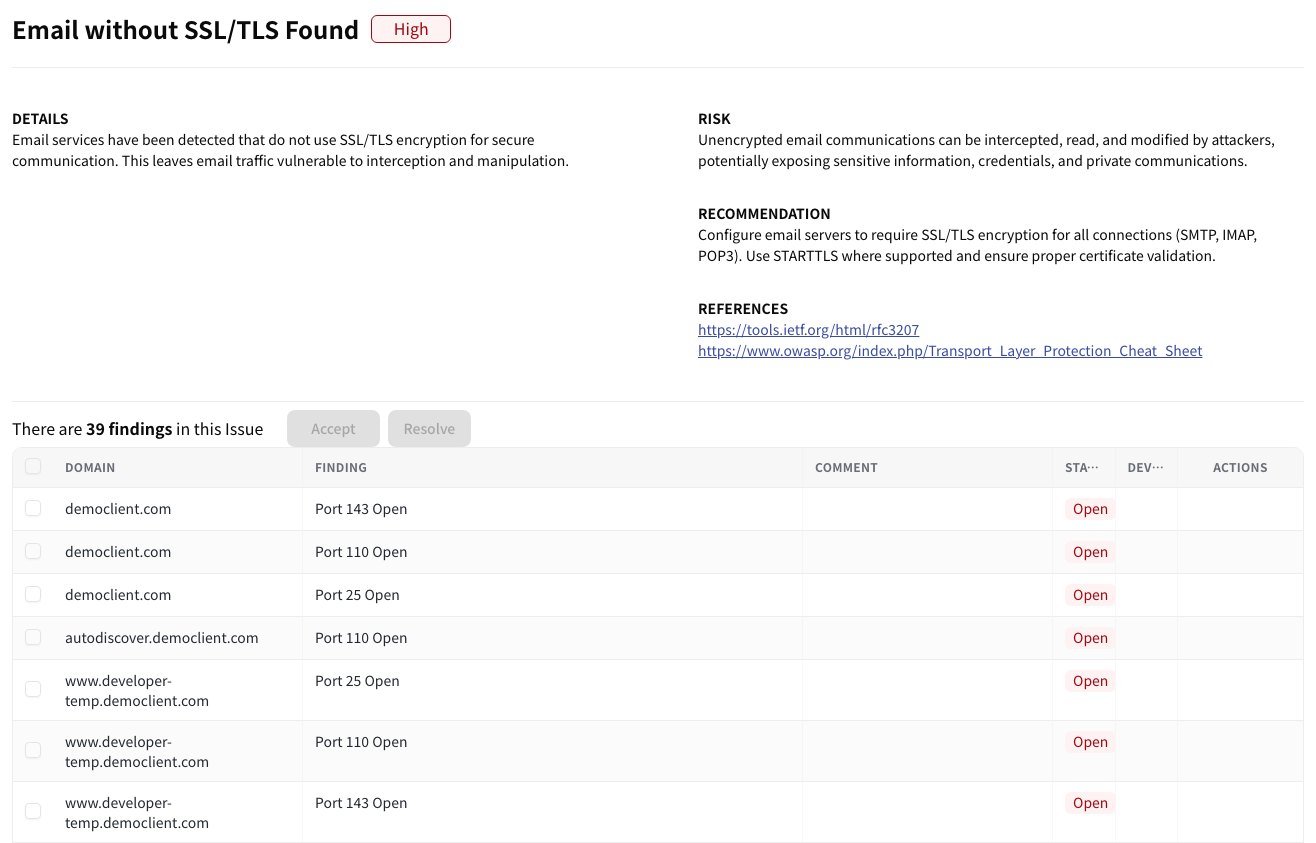
Ports this finding can list
Port 110 (POP3)
Port 110 (POP3)
POP3 downloads email from a server.Risk: POP3 on port 110 sends everything, including the password, in plain text, so
it can be read by anyone intercepting the traffic. POP3 over SSL (POP3S on port 995)
encrypts the connection.What to do: Check whether anyone still uses POP3. If they do, move them to POP3S on
port 995 and close port 110.
Port 143 (IMAP)
Port 143 (IMAP)
IMAP reads and manages email on a server.Risk: Like POP3, IMAP on port 143 sends data in plain text. IMAP over SSL (IMAPS on
port 993) encrypts it. How much damage a leaked login could do depends on what the
account can access.What to do: Check whether IMAP is in use and how sensitive the mailboxes are. Move
clients to IMAPS on port 993 and close port 143.
Port 25 (SMTP)
Port 25 (SMTP)
SMTP sends email between servers, and port 25 has to be open for anyone on the internet
to deliver mail to the company.Risk: A badly configured SMTP server can be abused by spammers to relay mail, and
weak authentication lets outsiders send mail through it.What to do: Decide whether the company needs to run its own SMTP server. If it does,
require encryption with STARTTLS, enforce authentication (for example SASL), and block
open relaying.