

Overview
Alerts tell you about a specific change as soon as Telivy finds it, such as a new dark web breach, a look-alike domain, a new critical vulnerability on an endpoint, or a Microsoft 365 account without MFA. Alert policies decide two things for each category: which of your team members get an email, and whether matching findings open a ticket in your connected PSA. Policies are set once for the whole agency and apply to every assessment.The Alerts page
Open Alerts in the Telivy portal to see every alert raised across your clients, newest first. Each row shows:
Clicking an alert that belongs to a finding opens the assessment’s Risk tab filtered to that finding, where you can accept it, resolve it, or open a PSA ticket. Other alerts open their own details page.
Use the filters to show unread alerts, a single category, or a time window such as In the last 7 days. Mark N as read clears the unread markers, and the chart button shows Alerts over time. Each assessment also has its own Alerts tab with the same list for that client.
Alert email
Alerts are emailed once an hour as a digest, so a busy hour produces one email instead of one per finding. Only users selected on a policy receive it. The digest groups alerts by client. For each alert it shows the risk level, what was detected, the affected device or account, the evidence behind it, a short recommended action, and a link to investigate in Telivy. Activity records, such as sign-in events, follow under their own heading so they are not mistaken for open risks. When a client has more alerts than fit, the email says how many more are waiting in the portal.Alert policies
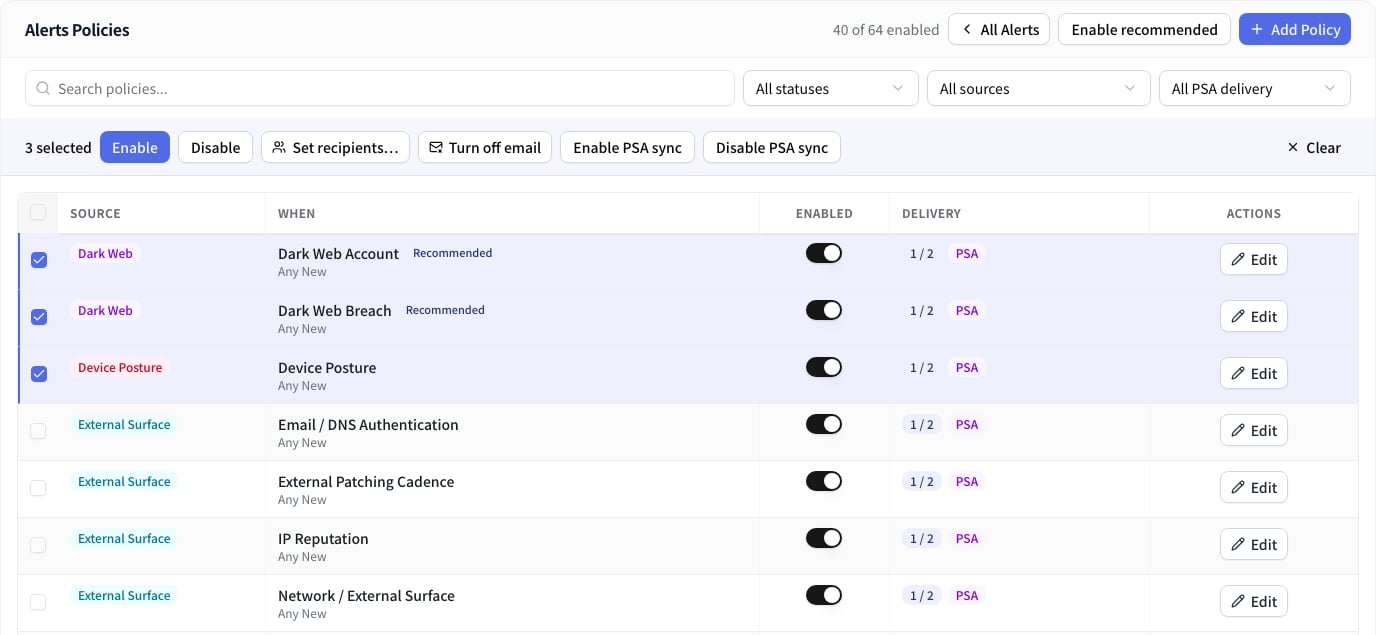
Go to Alerts → Policies. The page lists every alert category in one table, grouped by source (for example Dark Web, TypoSquatting, Internal Vulnerabilities, Microsoft 365 and Google Workspace), with a count of how many are enabled.
Search by name, or filter by source, by enabled status, or by PSA delivery.
Turn on the recommended set
Click Enable recommended to add policies for every recommended category that does not have one yet. The Apply recommended policies dialog shows how many categories and users it will add. Existing policies are not changed, so it is safe to run again after Telivy adds a category.Add or edit a policy
- Click Add Policy, or Edit on an existing row.
- In Configure Alert Policy, choose the Alert Category and the Trigger Condition. Some categories take an Alert Metric and a Value, for example a CVSS or EPSS threshold for Internal Vulnerabilities.
- Click Next: Select Users.
- In Configure Alert Delivery, choose the people to email. If a PSA is connected, its switch also opens tickets for this category’s findings. If not, this step offers to connect one.
- Click Save.
Change many policies at once
Tick rows to select them, then use the bar above the table:- Enable or Disable the selected policies. Disabling keeps the policies in the list, but their recipients are not kept.
- Set recipients… makes every selected policy email exactly the users you pick.
- Turn off email removes every recipient from the selected policies without touching PSA ticket sync.
- Enable PSA sync or Disable PSA sync for the selected categories.
Send findings to your PSA
With ConnectWise, Autotask or HaloPSA connected, alert policies also decide which findings open PSA tickets. Turn on PSA sync for a category from Edit (the switch named after your PSA in the Delivery step) or with Enable PSA sync in bulk. The Delivery column then shows PSA with the severity floor, such as High and above. PSA sync covers every finding category in the list, including external-surface ones such as Email / DNS Authentication or Web Application Security that do not send alert emails yet. A ticket is only opened when the client’s company is mapped to the PSA and Sync findings to PSA is on for its assessment. By default each finding opens its own ticket. To receive one ticket per scan for a category instead, use the ticketing button at the top of the page, which carries your PSA’s name. See Grouped PSA tickets.Alert categories
Every category appears in Alerts → Policies. These categories raise alerts today:Rolling out
The other Microsoft 365 and Google Workspace categories in the list are being rolled out and do not raise alerts yet. They include Authentication Token Revoked, MFA Failed, MFA Disabled, MFA Enabled, Password Reset, Login Using Token, Login From Unapproved Location, User Create, User Delete, Registered Device, Admin Role Assignment, Group Membership Change, and Admin Policy Change, plus Conditional Access Violation for Microsoft 365 only. Microsoft 365 mailbox and file activity categories, such as Mailbox Forwarding Rule Created, External File Sharing and Mass File Deletion, are also in the list ahead of their rollout. You can create policies for these categories now, and they start firing once the category goes live.FAQ
How quickly does an alert fire after an event is detected?
How quickly does an alert fire after an event is detected?
Cloud events (Microsoft 365, Google Workspace) are evaluated on each sync. Endpoint alerts such as Internal Vulnerabilities are evaluated after each completed agent scan, and a manual rescan triggers evaluation straight away. The alert shows on the Alerts page as soon as it is raised. The email follows in the next hourly digest. See Scanning Schedule for when each kind of data is collected.
Can I notify several team members from one policy?
Can I notify several team members from one policy?
Yes. Select as many agency users as you need in Configure Alert Delivery, or use Set recipients… to set them on several policies at once.
Are alert policies scoped to individual clients?
Are alert policies scoped to individual clients?
No. Policies are set at the agency level and apply to every assessment. Each assessment’s Alerts tab shows the alerts raised for that client.
Do alerts require Risk Monitoring to be enabled?
Do alerts require Risk Monitoring to be enabled?
No. Alerts are raised for any eligible Risk Assessment whenever new data arrives. Risk Monitoring adds the recurring rescans that keep that data fresh.
Can I stop the emails but keep PSA tickets?
Can I stop the emails but keep PSA tickets?
Yes. Select the policies and use Turn off email. PSA ticket sync on those categories keeps working.
Can I send alerts to another system?
Can I send alerts to another system?
Yes. Subscribe to the
ALERT_RAISED event with a webhook to receive each alert as an HTTP request.