

Generating a report
1
Open the report picker
In the assessment, open Reports and click Generate New Report.
2
Choose a report type
Pick the report from the list. You can type to search it.
3
Add contact details (Complete Report only)
For the Complete Report (PDF), expand Add Contact Info (Optional) and enter the
name, email, and phone number the client should contact about the report.
4
Generate
Click Generate Report. The new version appears at the top of the reports table.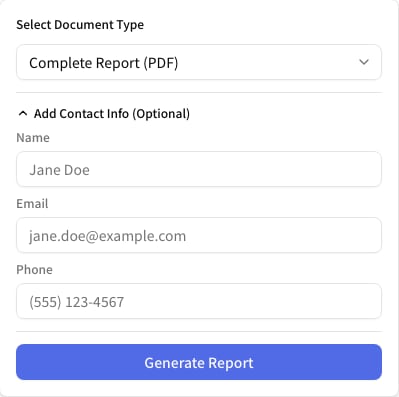
Which reports are available
The list depends on the assessment type, because most reports need data that an External Scan never collects.From an External Scan
- External Scan Executive Report (PDF)
- External Scan Detailed Report (PDF)
- Questionnaire Report (PDF)
- Progress Report (PDF and DOCX)
From a Risk Assessment
All of the External Scan reports, plus the ones built on agent and cloud data:Executive Summary (PDF) only appears once the assessment has an AI-generated executive
summary. If it isn’t in the list, the summary hasn’t been produced yet.
What the Complete Report contains
The Complete Report is the full cyber security risk assessment (CSRA) for a client. Its table of contents is built from the data available, so a section with nothing to say is left out. In order, it can contain:- CSRA Methodology
- Executive Summary, when the assessment has an AI summary
- Progress Since Last Assessment, when there is an earlier assessment to compare with
- Overview
- Data Breach Cost Breakdown, when a breach cost estimate is available
- One section per CIS control category, with the controls in it
- Detailed Recommendations
- Top Remediation Actions
- Top Critical Assets & Why
- Strategic & Operational Priorities
- Addendums
What the Executive Summary contains
The Executive Summary (PDF) is the short version for people who won’t read the full report. It covers issue severity, the score with a summary, CIS compliance, key findings, suggested actions, strategic and operational priorities, and next steps. Pages without data are skipped.Report versions
The reports table has one row per report type, with Last Generated At and the number of Versions. Click a row, or Expand All, to see every version with its file name and generation time. Download Latest Version in the row’s Actions menu downloads the newest copy.Which report to send
For a prospect who hasn’t bought anything yet, send the External Scan Executive Report. It is short and needs no agent. Once they’re a client and the first full scan is done, send the Complete Report, and add the Executive Summary for readers who won’t get through the full report. For monitoring reviews, send the Progress Report, which shows what changed since the last scan instead of restating the whole posture. The Complete Report also carries a progress section once there is an earlier assessment. When you’re talking to the client’s IT team, send the CSV exports, which are meant for a spreadsheet.Understand the scoring
What the score in the report measures
Report grading criteria
How each section of the report earns its grade